
The world of cloud computing is constantly evolving, and with it, the landscape of data storage and management has shifted dramatically. Understanding the nuances of these changes – particularly regarding data retention policies and the implications for businesses – is crucial for maintaining compliance and minimizing risk. This article delves into the complexities of “Notice Of Default Template” implementations, exploring their purpose, impact, and best practices for organizations of all sizes. The core of this discussion revolves around the fundamental principles governing how data is handled and secured in cloud environments, and how businesses can proactively manage these policies to ensure they align with legal and regulatory requirements. Notice Of Default Template is not just a technical term; it represents a critical framework for responsible data stewardship. It’s a foundational element of many compliance programs, particularly those related to GDPR, CCPA, and other data privacy regulations. Ignoring these policies can lead to significant fines, reputational damage, and legal challenges. This article aims to provide a clear and practical guide to navigating this complex area.
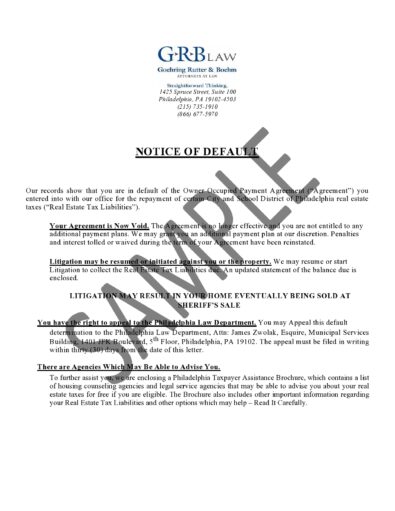
The rise of cloud computing has fundamentally altered how data is stored and accessed. Traditional on-premise data centers offered greater control but also presented challenges in terms of scalability, security, and compliance. Cloud providers, recognizing these shifts, have introduced sophisticated data management tools and policies. “Notice Of Default Template” represents a key component of these tools, designed to ensure that organizations understand and adhere to their data retention obligations. It’s a standardized approach to documenting and managing data lifecycle decisions, ensuring that data is handled appropriately throughout its existence. Without a clear understanding of these policies, businesses risk inadvertently violating regulations or exposing sensitive information. The implementation of “Notice Of Default Template” is not a one-time event; it’s an ongoing process that requires continuous monitoring, review, and adaptation.

Let’s begin by unpacking the core concept. “Notice Of Default Template” isn’t a single, monolithic policy; rather, it’s a collection of principles and procedures that govern how data is handled, stored, and deleted. It’s a contractual agreement between the organization and the cloud provider, outlining the provider’s responsibilities for data security and compliance. The template itself typically includes a detailed description of the organization’s data retention policies, including the types of data subject to retention, the retention periods, and the procedures for data deletion. It also addresses data access controls, encryption requirements, and incident response plans. The goal is to provide a clear and unambiguous framework for managing data throughout its lifecycle. Different cloud providers offer varying levels of “Notice Of Default Template” implementation, ranging from basic to highly comprehensive. Understanding these differences is essential for selecting the right provider and ensuring adequate protection for your data.
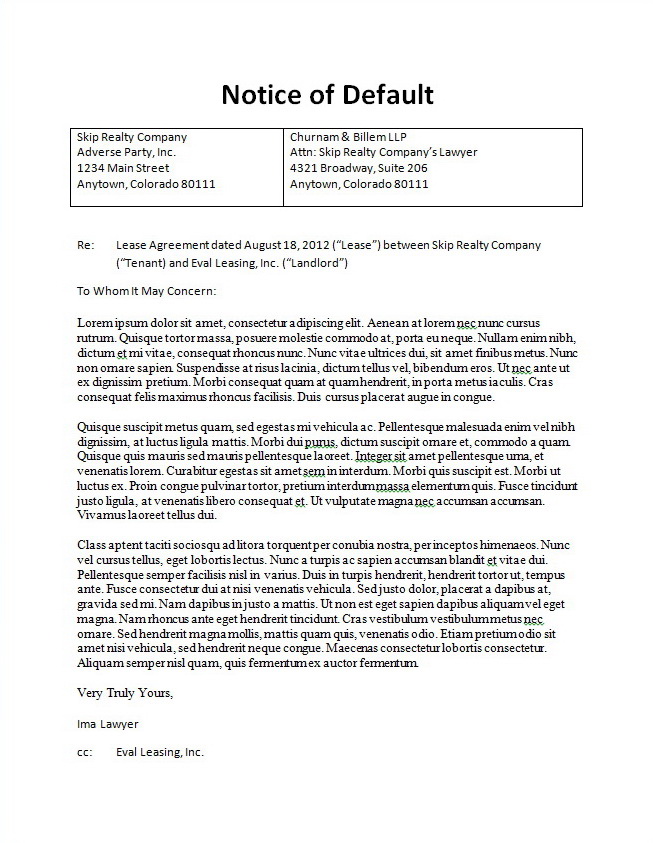
Understanding the Components of a “Notice Of Default Template”
A robust “Notice Of Default Template” typically encompasses several key elements. Firstly, it defines the types of data covered by the policy. This includes identifying specific data categories – such as customer data, financial records, or intellectual property – and establishing clear criteria for determining when data should be retained. Secondly, it outlines the retention periods for each data type. These periods are often based on legal requirements, industry best practices, and the specific nature of the data. For example, financial records might be retained for a longer period than marketing data. Thirdly, the policy details procedures for data deletion, including methods for securely wiping or destroying data to prevent unauthorized access. Fourthly, it addresses data access controls, specifying who has access to what data and under what conditions. This is critical for preventing accidental or malicious data breaches. Finally, it includes provisions for data incident response, outlining the steps to be taken in the event of a data breach or security incident.
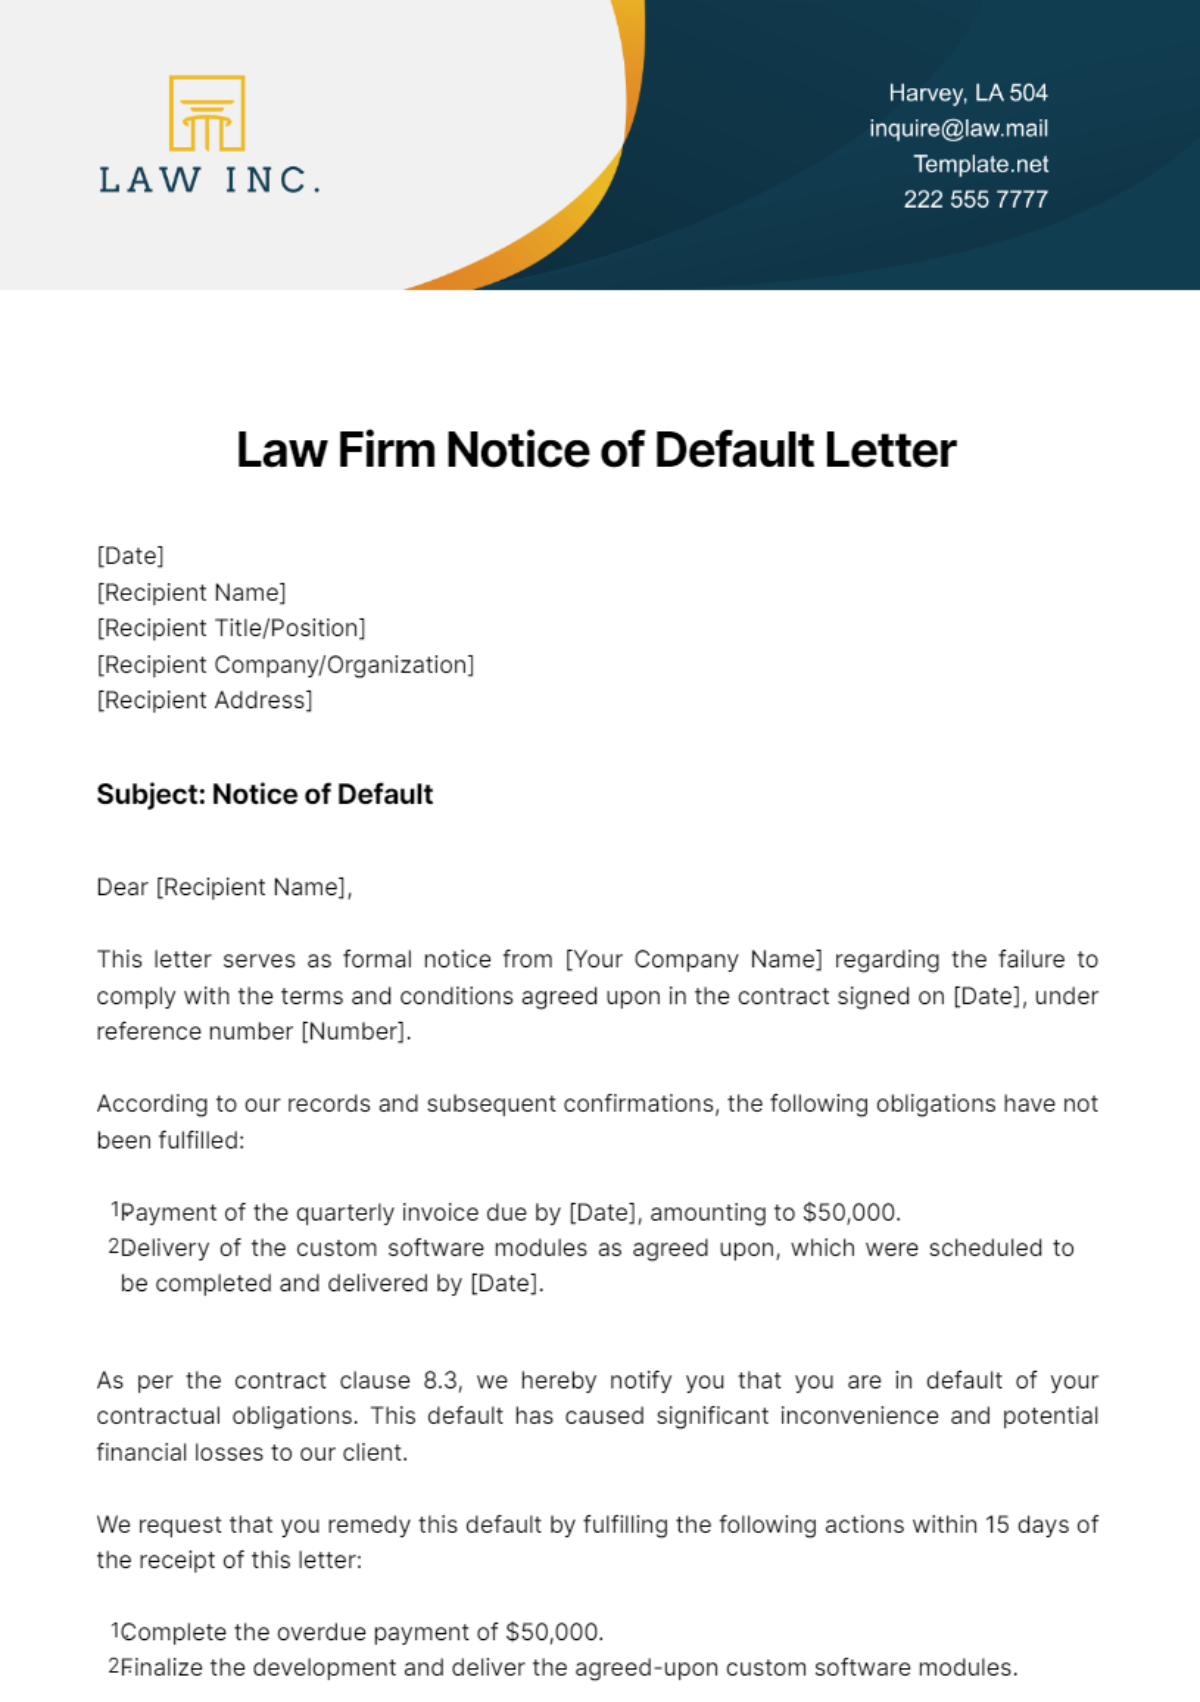
Key Areas Covered in a “Notice Of Default Template”
The specific content of a “Notice Of Default Template” can vary depending on the organization’s needs and the cloud provider’s offerings. However, several key areas are consistently addressed:
- Data Classification: This involves categorizing data based on its sensitivity and importance. “Notice Of Default Template” will detail how data is classified and the appropriate security measures for each classification level.
- Data Minimization: The policy should emphasize the principle of collecting only the data that is absolutely necessary for a specific purpose. This reduces the risk of storing unnecessary information.
- Data Security: This covers technical safeguards such as encryption, access controls, and intrusion detection systems. The “Notice Of Default Template” will specify the required security measures.
- Data Retention: As mentioned earlier, this defines the length of time data should be retained and the procedures for deletion.
- Data Breach Notification: The policy should outline the process for notifying affected parties in the event of a data breach.
- Data Subject Rights: This addresses the rights of individuals to access, correct, and delete their data. The “Notice Of Default Template” should detail how these rights are handled.
The Importance of a Well-Defined “Notice Of Default Template”
Implementing a comprehensive “Notice Of Default Template” is not merely a compliance exercise; it’s a strategic investment in data protection. Without a clear and documented policy, organizations are vulnerable to significant legal and reputational risks. Furthermore, a poorly defined policy can lead to inconsistent data handling practices, increasing the likelihood of security breaches and compliance violations. A well-crafted “Notice Of Default Template” provides a framework for consistent data management, reduces operational complexity, and demonstrates a commitment to responsible data stewardship. It’s a proactive approach that minimizes potential problems down the line.

Beyond the Template: Ongoing Monitoring and Review
Simply having a “Notice Of Default Template” is not enough. It must be actively monitored and regularly reviewed to ensure its effectiveness. Cloud providers offer tools and services that can automate data lifecycle management, helping organizations to stay on top of their compliance obligations. Regular audits of data retention practices are also essential. Organizations should conduct periodic reviews to ensure that their policies remain aligned with evolving regulations and business needs. Furthermore, employees should be trained on the “Notice Of Default Template” and their responsibilities for data management. A culture of data awareness and accountability is critical for maintaining a strong data protection posture.

The Role of Data Governance
Effective “Notice Of Default Template” implementation requires a robust data governance framework. Data governance encompasses policies, procedures, and organizational structures that ensure data is managed consistently and effectively. It’s about establishing clear roles and responsibilities for data ownership, stewardship, and security. A strong data governance framework provides the foundation for a successful “Notice Of Default Template” program. It ensures that data is treated as a valuable asset and that appropriate safeguards are in place to protect it.
Challenges and Considerations
Despite the benefits of a well-defined “Notice Of Default Template,” implementing and maintaining a robust policy can present several challenges. One common challenge is the complexity of cloud environments, which can make it difficult to track data across different providers. Another challenge is the rapid pace of technological change, which requires organizations to continuously update their policies and procedures. Furthermore, some organizations may lack the resources or expertise to effectively manage their “Notice Of Default Template.” Addressing these challenges requires a strategic approach, including investing in technology, training, and collaboration. It’s also important to recognize that “Notice Of Default Template” is not a one-size-fits-all solution. Organizations should tailor their policies to their specific needs and risk profile.

Conclusion
“Notice Of Default Template” represents a fundamental element of responsible data management in the cloud era. It’s a critical framework for ensuring compliance, minimizing risk, and protecting sensitive information. By understanding the purpose, components, and best practices for implementing a robust “Notice Of Default Template,” organizations can proactively manage their data lifecycle and safeguard their business interests. The ongoing monitoring, review, and adaptation of these policies are essential for maintaining a strong data protection posture. Ultimately, a well-defined “Notice Of Default Template” is an investment in the long-term success and sustainability of the organization. It’s a commitment to transparency, accountability, and a proactive approach to data stewardship. As cloud technologies continue to evolve, so too must our understanding and implementation of these critical policies.
[ssba-buttons]