
Implementing the ISO 27001 standard is a significant undertaking for any organization, demanding a structured approach to information security. The ISO 27001 policy template provides a robust framework for establishing and maintaining an effective information security management system (ISMS). This article will delve into the key components of these templates, offering practical guidance for organizations looking to achieve and maintain compliance. Understanding the nuances of these templates is crucial for ensuring a secure and resilient information environment. The core of this guide centers around the importance of tailoring the template to your organization’s specific needs and risk profile. It’s not a one-size-fits-all solution, but rather a starting point for a customized security strategy. Iso 27001 Policies Templates are designed to be adaptable, allowing for flexibility and continuous improvement. Let’s explore how these templates can be utilized effectively.
Understanding the Foundation: Why ISO 27001 Policies Templates Matter
The ISO 27001 standard isn’t just a set of rules; it’s a philosophy. It emphasizes a risk-based approach to information security, requiring organizations to systematically identify, assess, and mitigate potential threats. The ISO 27001 policy template provides the foundational structure for this process. It’s a living document, subject to regular review and updates to reflect evolving threats and best practices. Without a well-defined policy, organizations risk falling short of achieving the desired level of security, exposing valuable data and potentially facing significant financial and reputational damage. Furthermore, the template facilitates a consistent and repeatable approach to security management across the organization, promoting accountability and transparency. The initial investment in understanding and utilizing these templates pays dividends in the long run through reduced risk and enhanced operational efficiency.
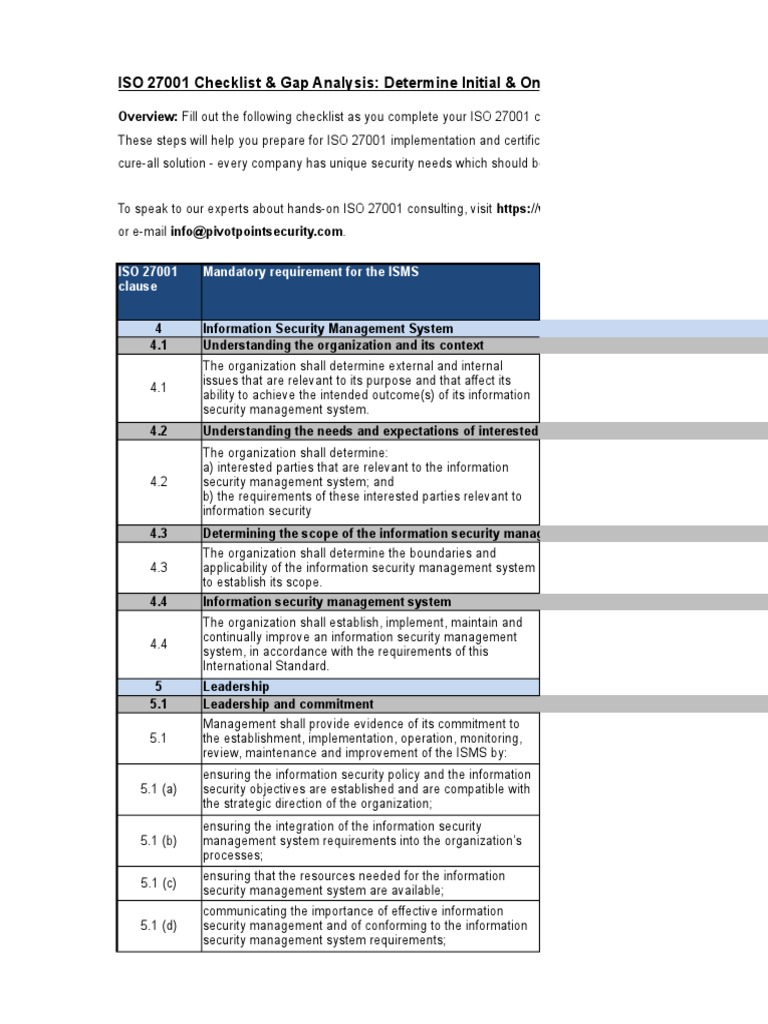
Core Components of an ISO 27001 Policy Template
A comprehensive ISO 27001 policy template typically includes several key sections. Each section addresses a critical aspect of information security. Let’s examine some of the most important elements:

1. Introduction and Scope
The introduction section clearly defines the purpose of the policy, its scope, and the organization’s commitment to information security. It outlines the objectives of the ISMS and the benefits realized through its implementation. The scope specifies which information assets are covered by the policy. This is a critical step in establishing the boundaries of the ISMS. Iso 27001 Policies Templates often include a statement outlining the policy’s applicability to specific departments or business units. A clear and concise introduction is paramount for ensuring everyone understands their role in maintaining the policy’s effectiveness.

2. Risk Assessment and Management
This section details the process for identifying, analyzing, and evaluating information security risks. It involves assessing the likelihood and impact of potential threats to information assets. The ISO 27001 framework emphasizes a risk-based approach, prioritizing risks that require the most attention. The template typically includes a risk matrix to visually represent the severity of risks. Iso 27001 Policies Templates often require organizations to document their risk assessment methodology and the rationale behind their risk prioritization. Regularly reviewing and updating the risk assessment is crucial to maintain its relevance.

3. Information Security Policies
This section outlines the specific policies that govern information security practices within the organization. These policies cover a wide range of topics, including access control, data protection, incident management, and business continuity. Iso 27001 Policies Templates often include detailed procedures for implementing and enforcing these policies. For example, a policy on data encryption should specify the types of encryption to be used and the procedures for key management.

4. Security Awareness and Training
This section emphasizes the importance of educating employees about information security risks and best practices. It outlines the training requirements and the methods used to deliver this training. A well-trained workforce is essential for preventing security breaches and responding effectively to incidents. The template may include a schedule for regular security awareness training. Iso 27001 Policies Templates often require documented training records for all employees.

5. Operational Procedures
This section details the specific operational procedures that support the information security policies. It covers topics such as system administration, network security, and incident response. Clear and documented procedures are essential for ensuring that security controls are effectively implemented and maintained. Iso 27001 Policies Templates often require the creation of detailed procedures for specific tasks, such as password management or data backup.

6. Monitoring and Audit
This section describes the methods used to monitor the effectiveness of the ISMS and to conduct audits. It includes procedures for logging security events, reviewing audit reports, and identifying areas for improvement. Regular monitoring and auditing are critical for ensuring that the ISMS is operating effectively and that security controls are maintained. Iso 27001 Policies Templates often require the establishment of a system for tracking security metrics and key performance indicators (KPIs).

Tailoring the Template to Your Organization
The ISO 27001 policy template is a starting point, not a rigid blueprint. It’s crucial to tailor the template to your organization’s specific needs and risk profile. Consider the following factors:

- Industry Regulations: Certain industries, such as healthcare and finance, are subject to specific regulatory requirements that must be addressed in the policy.
- Business Processes: The policy should align with your organization’s core business processes and workflows.
- Data Sensitivity: The level of sensitivity of the data you handle will influence the level of security controls required.
- Risk Appetite: Your organization’s risk appetite will determine the level of risk mitigation required.
Don’t hesitate to modify the template to reflect your unique circumstances. A flexible and adaptable policy is more likely to be successful than a rigid, one-size-fits-all approach.

Implementing and Maintaining the Policy
Once the ISO 27001 policy is developed, it’s essential to implement and maintain it effectively. This involves:

- Communication: Clearly communicate the policy to all employees and stakeholders.
- Training: Provide regular training on information security risks and best practices.
- Monitoring: Continuously monitor the effectiveness of the ISMS.
- Audits: Conduct regular audits to ensure compliance with the policy.
- Continuous Improvement: Regularly review and update the policy to reflect evolving threats and best practices.
Conclusion: A Secure Foundation for Success
Implementing the ISO 27001 policies template is a critical investment in the security and resilience of your organization. By understanding the key components of these templates, tailoring them to your specific needs, and consistently implementing and maintaining the policy, you can significantly reduce your risk of data breaches and ensure a secure and compliant information environment. The ongoing commitment to continuous improvement is paramount to maintaining a robust and effective ISMS. Remember, the ISO 27001 framework is a journey, not a destination. It requires ongoing vigilance and adaptation to remain effective in a constantly evolving threat landscape. Iso 27001 Policies Templates provide the foundation for this journey, empowering organizations to proactively manage information security and protect their valuable assets.
[ssba-buttons]