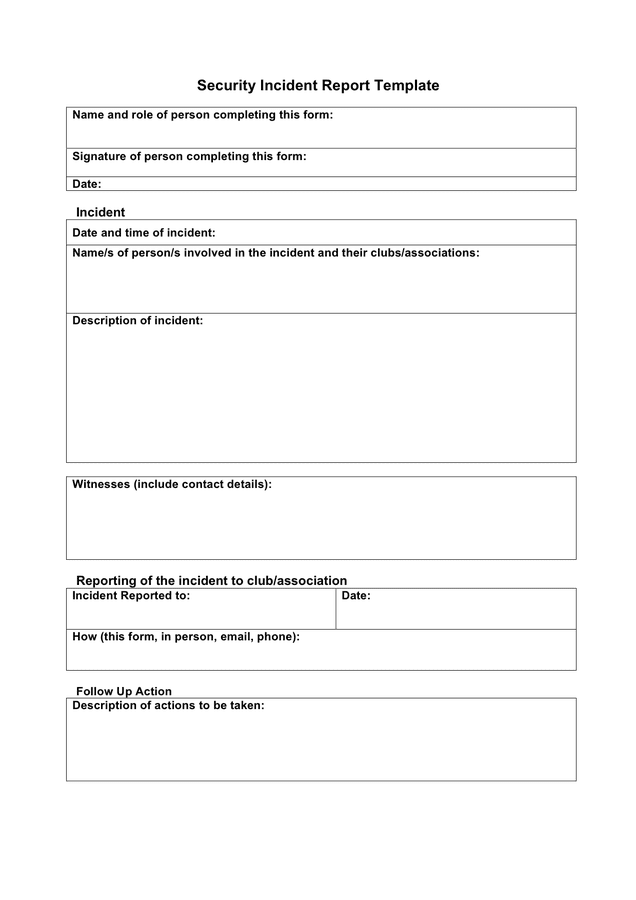
The escalating threat of cyberattacks demands robust and systematic approaches to detection, response, and recovery. A well-structured Cyber Security Incident Report Template is an essential tool for organizations to effectively document, analyze, and learn from security incidents. This template provides a standardized framework for capturing critical information, ensuring consistent reporting and facilitating informed decision-making. Cyber Security Incident Report Template is more than just a document; it’s a proactive strategy for minimizing damage and strengthening overall security posture. This article will delve into the key components of a comprehensive report, offering practical guidance on how to tailor the template to your specific needs and industry.
Understanding the Importance of Incident Reporting
The consequences of a cyber security incident can be devastating, ranging from financial losses and reputational damage to legal liabilities and operational disruptions. A timely and accurate incident report is crucial for several reasons. Firstly, it allows for a clear understanding of the scope and impact of the incident. Secondly, it facilitates forensic analysis to determine the root cause and identify vulnerabilities that may have contributed to the breach. Thirdly, it supports effective remediation efforts and prevents similar incidents from occurring in the future. Furthermore, regulatory compliance often mandates detailed incident reporting, adding another layer of importance to the process. Investing in a robust incident reporting system is, therefore, a strategic imperative for any organization operating in the digital landscape.

Core Components of a Cyber Security Incident Report Template
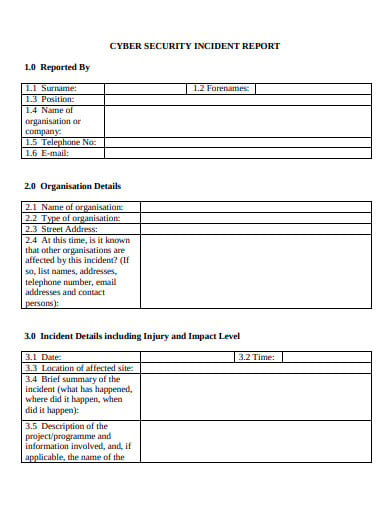
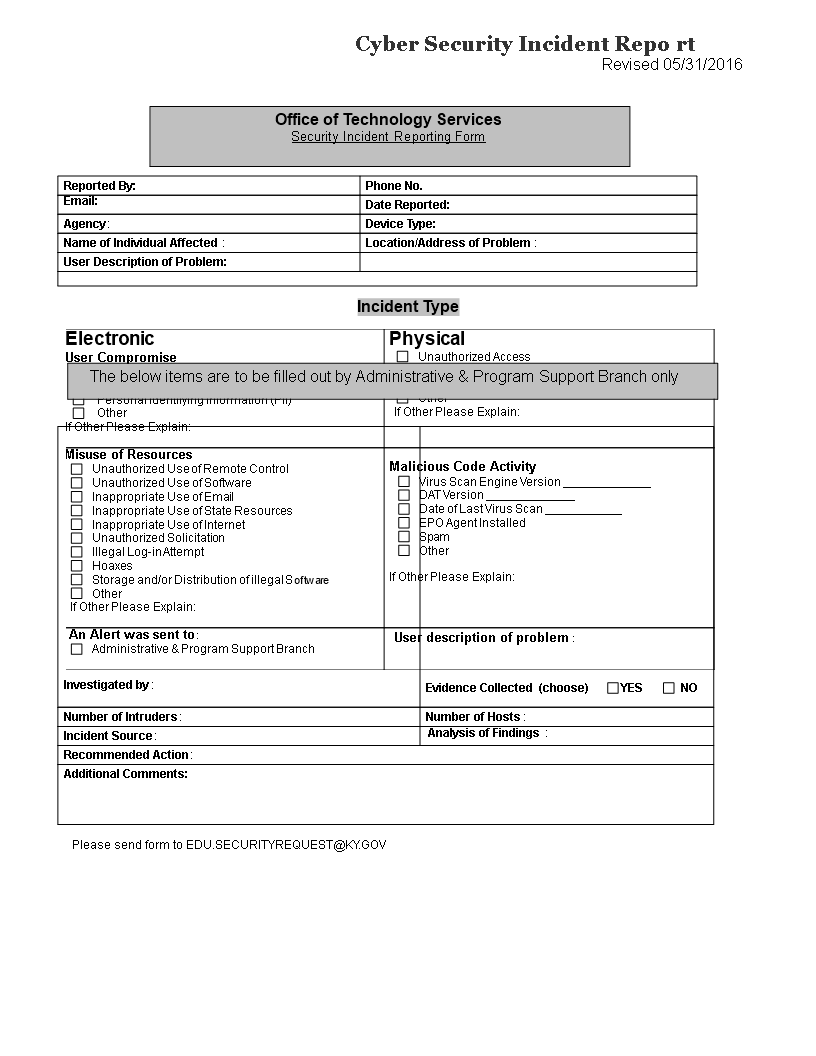
A comprehensive Cyber Security Incident Report Template typically includes the following sections. Each section should be clearly defined and populated with relevant details. The level of detail required will vary depending on the nature of the incident and the organization’s risk tolerance.
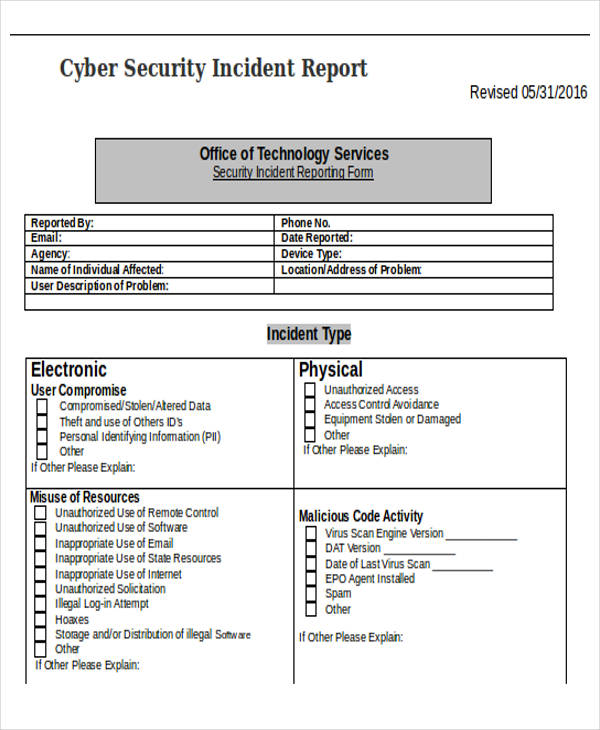
1. Incident Summary
This section provides a concise overview of the incident. It should include the following information:

- Date and Time of Incident: Precisely record the date and time the incident was detected.
- Type of Incident: Categorize the incident (e.g., malware infection, phishing attack, data breach, denial-of-service).
- Affected Systems/Assets: List the specific systems, applications, or data that were impacted.
- Initial Impact Assessment: A brief statement outlining the immediate consequences of the incident (e.g., data loss, system downtime, service disruption).
- Incident Severity Level: Assign a severity level (e.g., Critical, High, Medium, Low) based on the potential impact.
2. Incident Details
This section provides a detailed account of the incident, including technical information and observations.
- Source of the Incident: Identify how the incident was discovered (e.g., security monitoring system, user report, threat intelligence feed).
- Log Data: Include relevant log entries from affected systems, including timestamps, event descriptions, and error messages. This is critical for forensic analysis.
- Malware Analysis (if applicable): Describe the type of malware involved, its behavior, and any observed characteristics. Include screenshots and relevant analysis reports.
- Network Traffic Analysis: Document any unusual network activity that may be related to the incident. This could include suspicious traffic patterns, data exfiltration attempts, or unauthorized access.
- User Activity: Record any suspicious user actions that may have contributed to the incident.
3. Response Actions Taken
This section details the steps taken to contain, eradicate, and recover from the incident.

- Containment Measures: Describe the actions taken to isolate affected systems and prevent further spread of the incident (e.g., network segmentation, system shutdown, firewall rules).
- Eradication Procedures: Outline the steps taken to remove the malware or other malicious components from affected systems.
- Recovery Efforts: Detail the process of restoring affected systems and data to a normal state.
- Communication Plan: Document the communication strategy employed to inform stakeholders (e.g., internal teams, management, customers, regulatory authorities).
4. Root Cause Analysis
This section is arguably the most important, as it aims to determine why the incident occurred.
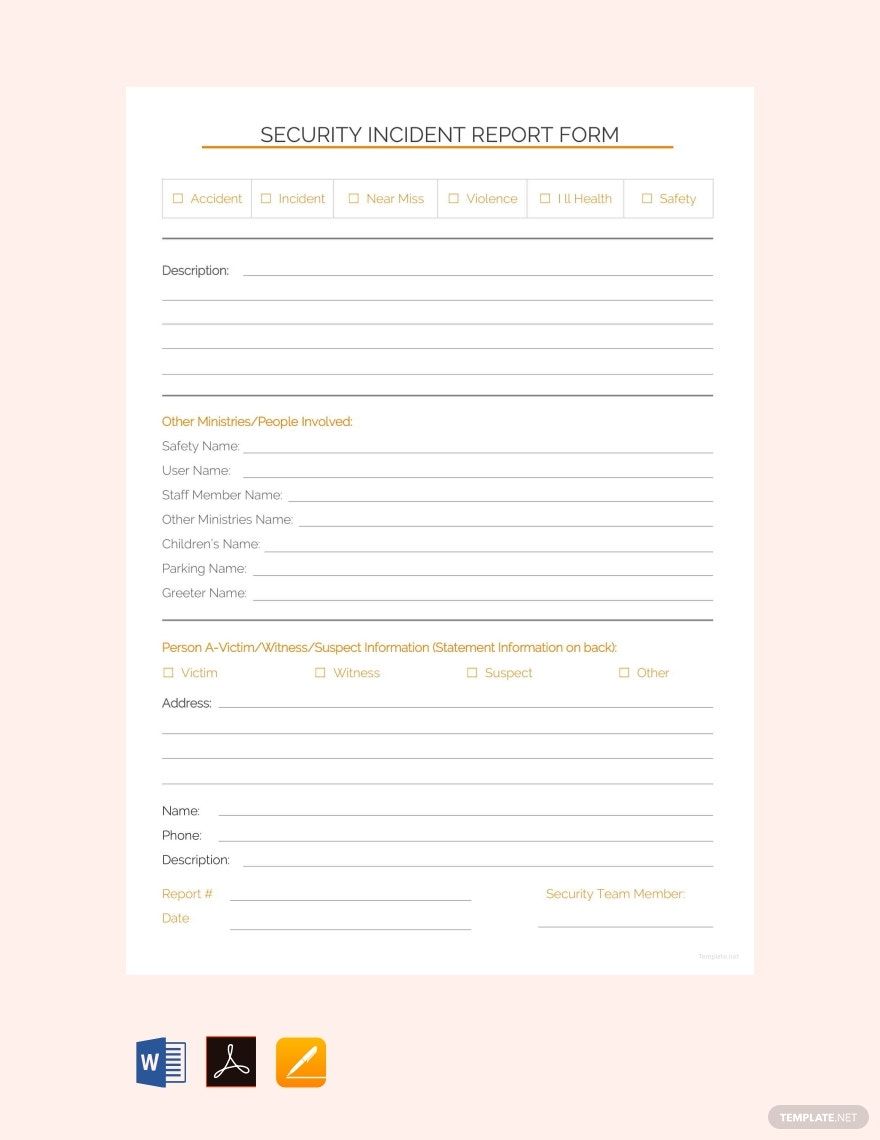
- Potential Root Causes: Identify potential factors that may have contributed to the incident (e.g., unpatched vulnerabilities, weak passwords, phishing attacks, insider threats).
- Vulnerability Assessment: Assess the extent to which vulnerabilities were exploited.
- Security Controls Review: Evaluate the effectiveness of existing security controls (e.g., firewalls, intrusion detection systems, antivirus software).
- Lessons Learned: Document key takeaways and recommendations for preventing similar incidents in the future.
5. Recommendations
This section provides actionable recommendations for improving security.
- Security Enhancements: Suggest specific security improvements to mitigate future risks (e.g., patching vulnerabilities, strengthening password policies, implementing multi-factor authentication).
- Process Improvements: Recommend changes to existing security processes and procedures.
- Training and Awareness: Recommend training programs to enhance employee awareness of security threats.
- Vendor Risk Management: Assess the security posture of third-party vendors.
Conclusion
Cyber Security Incident Report Templates are invaluable tools for organizations seeking to proactively manage and mitigate cyber risks. By systematically documenting incidents, analyzing their root causes, and implementing effective remediation strategies, organizations can significantly reduce their vulnerability to attacks and protect their valuable assets. A well-crafted template, coupled with a commitment to continuous improvement, is a cornerstone of a robust cybersecurity program. The consistent application of this template, alongside regular audits and vulnerability assessments, will contribute significantly to a more secure digital environment. Cyber Security Incident Report Template is a dynamic document, requiring ongoing adaptation to reflect evolving threats and organizational needs.
Conclusion
The importance of a comprehensive Cyber Security Incident Report Template cannot be overstated. It’s not simply a bureaucratic exercise; it’s a critical component of a layered security strategy. By diligently following the outlined structure and incorporating best practices, organizations can significantly enhance their ability to detect, respond to, and recover from cyber incidents, ultimately safeguarding their critical assets and maintaining operational resilience. Investing in the right tools and processes, including a well-designed Incident Report Template, is a fundamental step towards a proactive and secure future.
[ssba-buttons]